 LibreChat
Authentication
How people sign up and sign in to LibreChat, from email and password to social logins, SSO, LDAP, two-factor authentication, and passkeys.
Every LibreChat user signs in before they can chat; there is no guest mode. Out of the box that means an email and password, and an admin can add social logins, OpenID Connect or SAML single sign-on, and LDAP on top of it or in its place.
Signing up and signing in
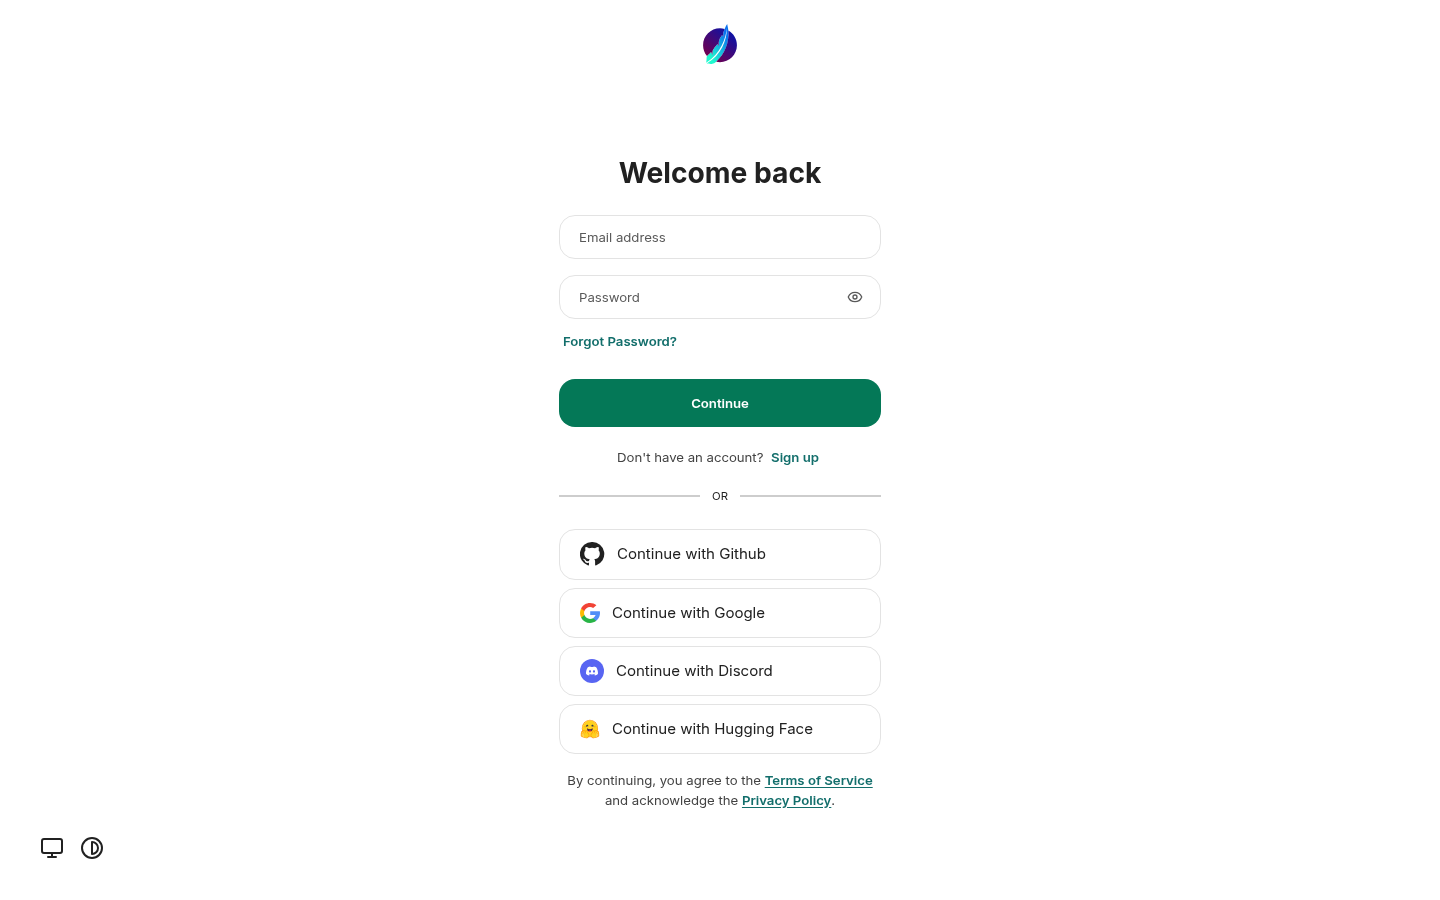
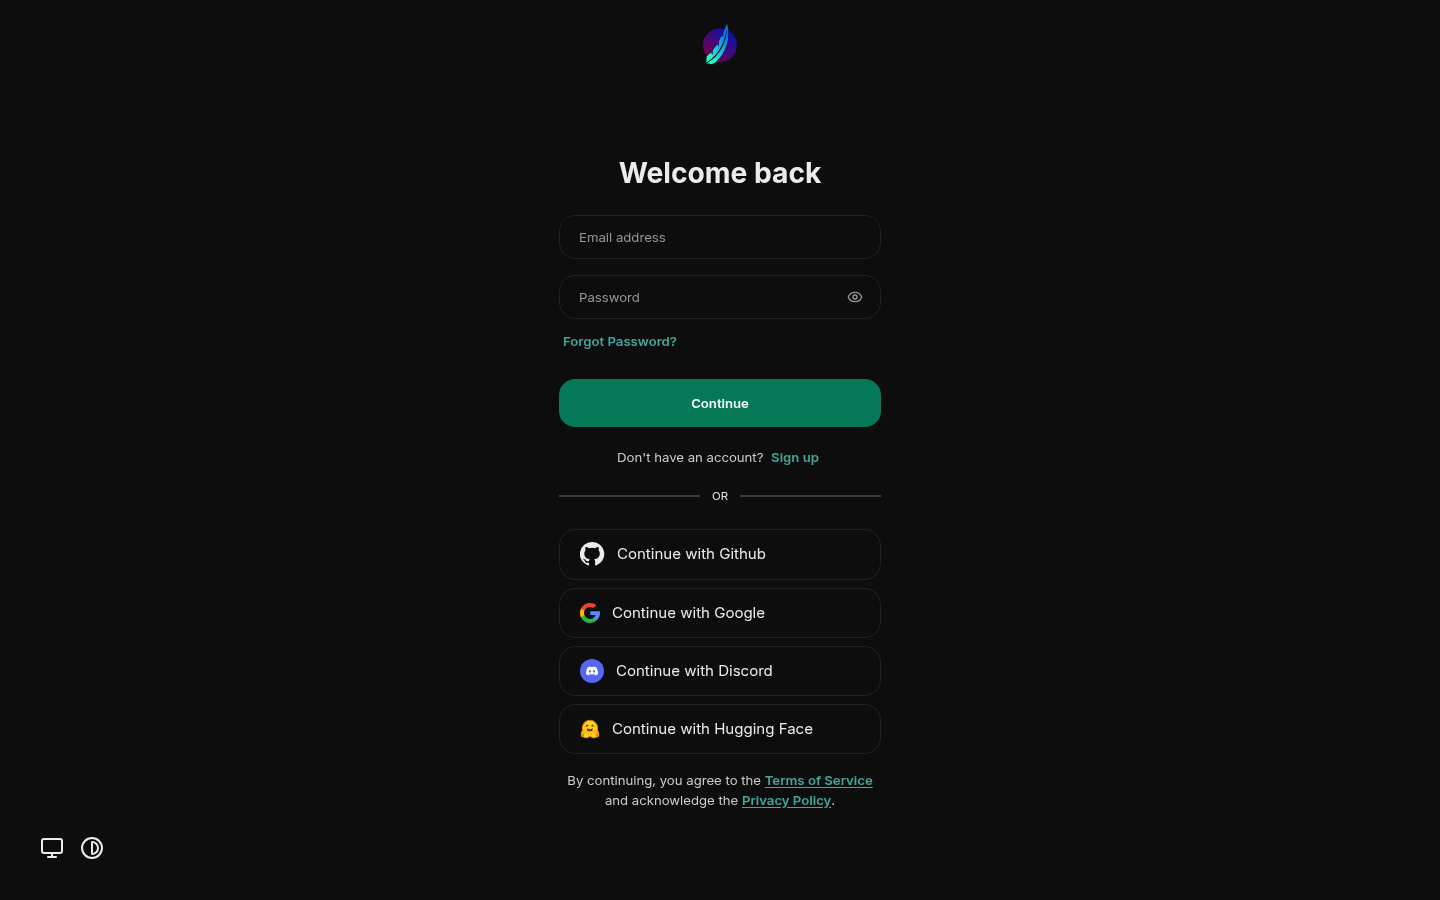
The login page shows the email and password form, a Forgot Password? link when password reset is enabled, and one button per enabled provider (Continue with Google, Continue with Github, Continue with Discord, Sign in with Apple, and so on). New users follow Sign up under "Don't have an account?" to reach the Create your account form, which asks for a full name, an optional username, an email, and a password of at least 8 characters.
On a single-tenant instance, the first account ever created becomes the admin. Create it yourself, right after the first start, and make it a local email and password account so you can still get in if an identity provider is misconfigured. Every later account gets the default USER role. Multi-tenant deployments never promote a first user; tenant admins are set up by the operator. See Access Control for what roles control.
When an email service is configured, registration sends a verification link. Whether an unverified user can sign in before clicking it is up to the admin; if they cannot, they see "Your account has not been verified" and can request a new link with Resend Email.
If an admin has limited sign-ups to certain email domains, users from other domains are turned away, and that applies to social and SSO logins too, not just the registration form.
Social logins and single sign-on
Social and SSO buttons only appear for providers the admin has configured. Signing in with a provider for the first time creates a LibreChat account linked to that identity, unless social registration is turned off, in which case only users who already have an account can use it.
Supported providers include Google, GitHub, Discord, Facebook, Apple, any OpenID Connect provider (Entra ID, Keycloak, Auth0, Authentik, Cognito, and others), SAML, and LDAP or Active Directory. With OpenID token reuse enabled on Entra ID, a user's Entra group memberships are synced into LibreChat at each login, which makes those groups available for sharing.
Two-factor authentication
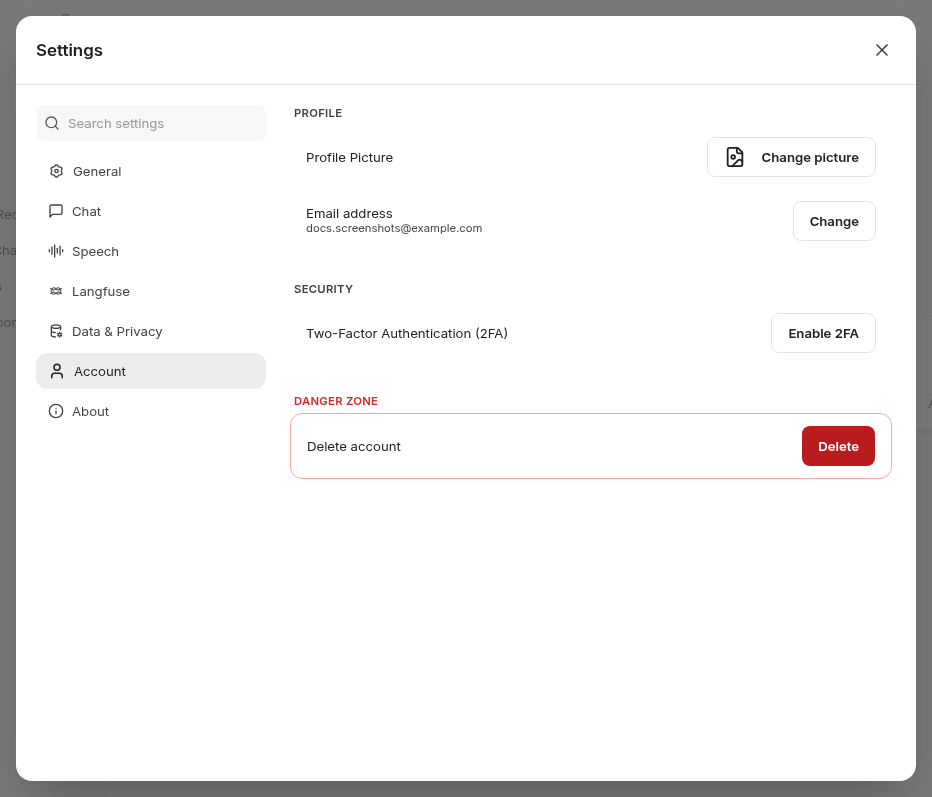
Users with an email and password or LDAP account can turn on 2FA from Settings > Account > Two-factor authentication. Setup walks through scanning a QR code with an authenticator app, confirming a code, and saving Backup Codes, which are shown only once. After that, signing in asks for a code from the app, or a backup code instead. Accounts that sign in through a social provider or SSO do not see the setting, since their identity provider handles MFA.
An admin can make 2FA mandatory. Users who have not set it up are stopped on a Two-Factor Authentication Required screen right after signing in and must finish setup before they can use LibreChat. Once it is required, the disable control shows Required by administrator and 2FA cannot be turned off.
Changes to 2FA from Settings (enabling, verifying, disabling, regenerating backup codes) share a budget of 7 requests per 5 minutes per account by default, successful ones included. Going over it shows a message telling you when to try again; it does not mean your code was wrong.
Passkeys
When an admin enables them, users can add a passkey (a device screen lock, a password manager, or a security key) under Settings > Account > Passkeys with Add passkey, then use Sign in with a passkey on the login page instead of a password. Adding and removing a passkey both ask for the account password first. If the account also has 2FA, the code is still asked for after a passkey sign-in.
Changing your email address
Email and password users can change their address under Settings > Account > Email address with Change. In the Change email address dialog, enter the new address and your current password, then Send verification link.
- Nothing changes until you open the link sent to the new address. It works once and expires after 15 minutes by default, and changing your password before opening it invalidates it.
- The current address gets a security notice as soon as a change is requested, and both addresses get a notice once the change goes through.
- The new address cannot belong to another account, and it has to be in the allowed domains if the admin set any.
The option only appears when the server can send email and the admin has not turned it off.
Staying signed in
A session renews itself in the background, so you are not asked to log in every 15 minutes even though that is how long an access token lasts. What ends a session is the refresh window, 7 days by default, counted from when you logged in: staying active does not extend it. You are also signed out if you choose Log out, if the browser drops the session cookie, or when your password is reset, which signs the account out everywhere.
With OpenID token reuse turned on, the session follows your identity provider's refresh token instead, so the provider's lifetime and revocation rules decide when you are signed out.
Reading a shared link is the one thing that can work without an account, and only if the admin allows public shared links.
Setup
Email and password sign-up and login are on by default; social logins are off until an admin configures a provider. Everything here is set up by an admin: start with Authentication configuration (including required 2FA and session lengths), then the guides for OAuth2 and OpenID Connect, SAML, LDAP, passkeys, and email (which also covers email address changes). Domain restrictions and the order of the login buttons live in the registration block of librechat.yaml.
How is this guide?
Import and Export Conversations
Bring your chat history into LibreChat from ChatGPT, Claude, ChatbotUI v1, or another LibreChat instance, and export a conversation as Markdown, text, JSON, CSV, or an image.
Access Control
Who can use which features, who can see and edit a shared agent, prompt, or MCP server, and how admin powers can be handed out.